A VPN (virtual private network) creates an encrypted connection between your device and a VPN server. It is useful when you need private access to a network, want traffic to leave from a chosen IP address, or do not want the local network to see the destinations reached through the tunnel. It is a routing and trust choice, not a button for anonymity or universal safety.
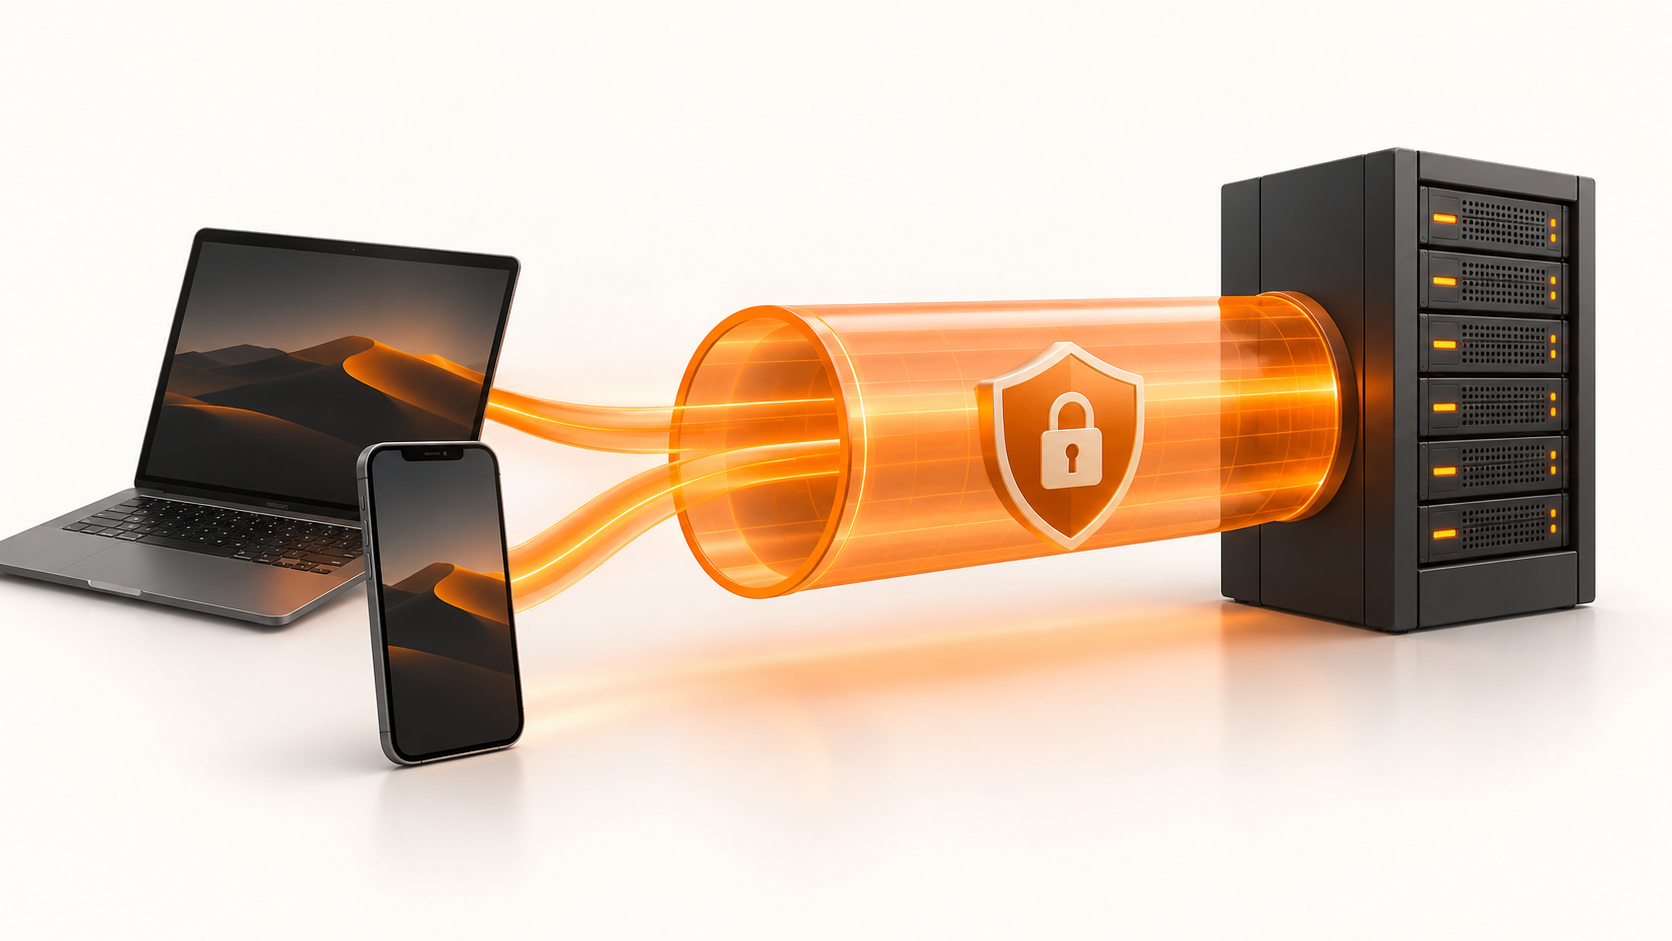
How does a VPN work?
Your device sends selected traffic through an encrypted tunnel to a VPN server. The server forwards it to the destination. The local network can generally see that you connected to a VPN server, while the destination sees the server’s public IP address rather than your home or mobile IP. The VPN operator can see connection metadata and may see traffic that is not separately encrypted.
A full-tunnel configuration routes general internet traffic through the VPN; a split tunnel routes only selected networks or applications. Either way, HTTPS remains important: it protects the connection between your browser and the website, including beyond the VPN server.
When is a VPN actually useful?
Access a private network remotely
Connect employees or your own devices to internal tools without exposing every application directly to the internet. Restrict who can join, keep software patched and still enforce access controls on the applications themselves. A VPN does not replace authentication.
Use an exit point you control
A self-hosted VPN on a VPS gives your devices a consistent server IP for outbound traffic. That can help with allowlisted administration tools, testing how a service behaves from another region, or accessing your own resources while travelling. Websites can identify and block data-centre IPs, so a VPN cannot guarantee a streaming catalogue, a particular website, or CAPTCHA-free access.
Limit what the local network can inspect
On a network you do not trust, a correctly configured VPN can conceal the destinations and unencrypted traffic sent through it from the local operator. Most modern websites already use HTTPS, which protects page contents and credentials without a VPN. A VPN can add a different layer of protection for selected metadata and other applications, but shifts trust to the VPN endpoint.
Operate a VPN service
A business can run VPN endpoints for customers, but it must handle accounts, abuse reports, updates, monitoring and support. EDIS Global welcomes commercial VPN operators on its KVM VPS; the infrastructure and your service responsibilities are different. Read the commercial deployment guide.
What a VPN cannot do
- It cannot make you anonymous. Websites can still recognize logins, cookies, device fingerprints and information you share. Your VPN and hosting providers may hold account and connection information.
- It cannot guarantee access through censorship or geo-blocks. Networks may detect or block VPN protocols or server IPs, and destinations decide whether to accept a connection.
- It cannot remove malware, phishing or weak passwords. Keep your devices updated, use multi-factor authentication and check the site you are visiting.
- It cannot encrypt traffic after the VPN exit on its own. Use HTTPS or other end-to-end encryption for sensitive data.
For a fuller threat-model discussion, see the Electronic Frontier Foundation’s guide to choosing a VPN.
Self-hosted VPN or subscription service?
With a subscription service, the provider maintains the software and typically offers many exit locations. You depend on its policies and operation. With a VPN on your own VPS, you choose the protocol, users, keys, logs and server location, and can keep a stable IP. You also take responsibility for securing, updating and monitoring it. The hosting provider still operates the underlying infrastructure; self-hosting is not an anonymity guarantee.
Choose the option that solves your actual problem. For access to your own applications or a fixed business IP, a single VPS can be enough. If you need a consumer app with one-click switching among many locations, running your own server involves more work.
A practical VPS setup checklist
- Pick a location based on the route from your users, not just the map. A distant server adds latency, and available performance depends on the entire path and your plan.
- Choose maintained VPN software such as WireGuard or OpenVPN, install it on a supported Linux system and create separate credentials or keys for each user. Keep the OS and VPN updated.
- Decide whether you need a full or split tunnel. Configure firewall rules, DNS and IPv4/IPv6 routing deliberately; test which traffic still goes out directly.
- Test the public exit IP, DNS resolution and reconnect behavior from a real client network. If uninterrupted tunnelling matters, configure and test a client-side kill switch.
- Budget both directions of VPS transfer. A 100 GB download sent to a VPN user enters the VPS and leaves it again: about 200 GB against the allowance, plus VPN overhead.
Running a VPN on EDIS Global
EDIS Global’s KVM VPS give you root control and a public IP at a selected location. They support VPN software including WireGuard, OpenVPN and IPsec; you install and operate the service. Compare current KVM VPS options and VPN hosting locations before choosing the resources and traffic allowance.
Each VPS has a monthly traffic allowance. If it and the grace allowance are exhausted, service stays online with no automatic overage charge, but traffic is normally limited to approximately 1 Mbps until more traffic is assigned or the allowance resets. That is too slow for a busy VPN. Read the traffic policy and monitor usage.
Common questions
Will a VPN hide my identity?
No. It changes the IP address seen by a destination, but an account login, cookies, payments or device identifiers can still link activity to you. The VPN endpoint becomes another party you must trust.
Do I need a VPN whenever I use public Wi-Fi?
Not always. HTTPS already protects most web content in transit. A VPN may help if you do not trust the network operator or need access to a private network; weigh that benefit against the trust you place in the VPN operator.
What happens if my VPN disconnects?
That depends on your client settings. Without a kill switch or restrictive routes, traffic may resume over your ordinary connection. Test failure and reconnection before relying on the tunnel for sensitive work.
Can I always bypass a block with my own VPS?
No. Some networks block VPN connections, and some services reject data-centre IP addresses. Reachability varies by network, destination and time. Test the exact route you need and follow applicable rules.